About
Security engineer who ships
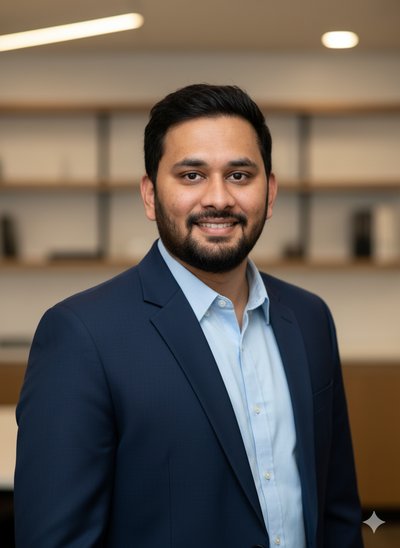
I'm Salman Tabrez, a cloud security and DevSecOps engineer based in Chicago. I secure cloud-native applications and infrastructure across the delivery lifecycle, from architecture review to production monitoring, on AWS, Azure and GCP.
I start with the threat model, not the tool: identify what needs protection, map trust boundaries, then pick controls that match the risk. I automate repetitive security work so engineering teams stay fast without cutting corners.
How I work
- 01
Assess
Identify assets, map data flows and trust boundaries, and model threats with STRIDE before implementation starts.
- 02
Embed
Add SAST, SCA, DAST and IaC scanning to CI/CD with automated gates, so security is a build step.
- 03
Harden
Apply least-privilege IAM, network segmentation and encryption at rest and in transit. No default credentials.
- 04
Detect
Write detection rules mapped to MITRE ATT&CK, tune thresholds and build response playbooks.
- 05
Automate
Write Python tooling for IAM audits, compliance checks and remediation to remove manual work.
Areas of focus
Get in touch
Find me on LinkedIn or email salmantabrezmd@gmail.com.